PII management plays a central role in GDPR compliance because the regulation is built almost entirely around how organizations collect, store, process, and share personally identifiable information. Without a structured approach to managing PII, meeting GDPR obligations becomes guesswork rather than governance. The sections below break down what qualifies as PII under GDPR, how your management practices shape your compliance posture, and where the most serious risks tend to emerge.
What counts as PII under GDPR?
Under GDPR, PII refers to any information that can identify a living individual, either directly or indirectly. This is broader than many organizations initially expect. A name and email address clearly qualify, but so does a combination of seemingly anonymous data points that, when combined, single out a specific person.
GDPR uses the term “personal data” rather than PII, but the concept is the same. Common examples include:
- Names, email addresses, phone numbers, and physical addresses
- IP addresses, cookie identifiers, and device IDs
- Location data and browsing behavior tied to an individual
- Inferred attributes such as purchasing patterns or interests linked to a profile
The regulation also defines a special category of sensitive personal data, covering health information, biometric data, racial or ethnic origin, and similar attributes, which carry stricter processing requirements. Understanding exactly which data your organization holds is the first step toward meaningful GDPR compliance.
How does PII management affect GDPR obligations?
PII management directly shapes how well an organization can fulfill its core GDPR obligations, including lawful basis documentation, data subject rights, retention limits, and breach notification. Every GDPR requirement is, in essence, a requirement about how personal data is handled at each stage of its lifecycle.
Strong PII management practices enable organizations to respond to subject access requests within the required timeframe, demonstrate a lawful basis for every processing activity, and enforce data minimization so that only necessary information is retained. Without clear visibility into where PII lives across systems, these obligations become difficult to meet consistently.
Data mapping is particularly important here. Knowing which identifiers flow through which systems, who has access, and for how long gives compliance teams the foundation they need to enforce policies rather than simply document them.
What are the biggest PII management risks for GDPR non-compliance?
The biggest PII management risks for GDPR non-compliance are fragmented data storage, inadequate access controls, and poor data lifecycle governance. These gaps make it difficult to enforce consent preferences, respond to regulatory inquiries, or detect and report breaches within GDPR’s 72-hour notification window.
Fragmentation is particularly common in organizations that have grown through acquisitions or that operate across multiple marketing and analytics platforms. When personal data exists in siloed systems without a unified view, enforcing deletion requests or auditing processing activities becomes unreliable. Other significant risks include:
- Retaining data beyond its stated purpose without a documented justification
- Failing to update consent records when individuals withdraw permission
- Transferring personal data to third-party vendors without adequate data processing agreements
Each of these risks compounds over time. Regulators increasingly scrutinize not just whether a breach occurred, but whether the organization had reasonable controls in place before it happened.
How FullContact supports privacy-safe PII management
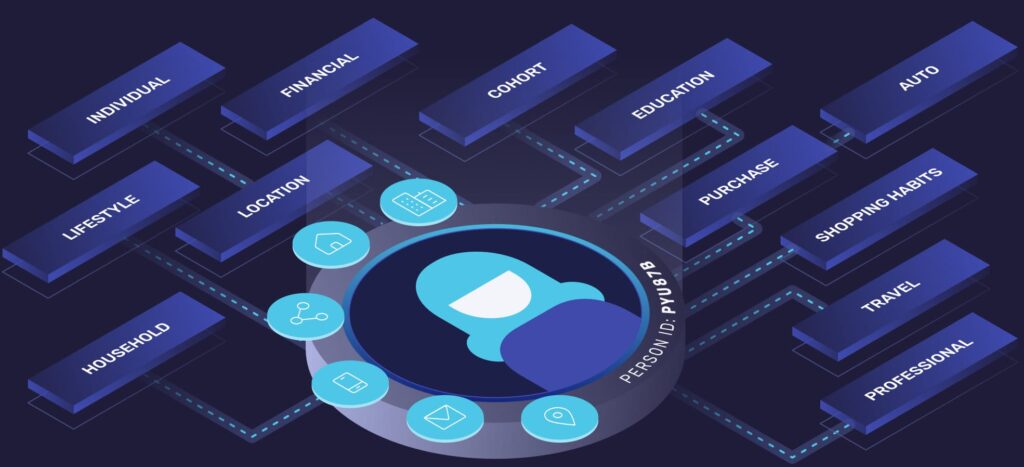
We built FullContact around the principle that identity resolution and privacy compliance are not in conflict. Our platform helps organizations bring fragmented personal data into a unified, structured view without exposing raw PII across systems. At the core of this approach is our identity graph, which connects disparate data points into a coherent, privacy-safe picture of each customer. Specifically, we help by:
- Resolving identifiers across devices and channels into a single customer profile, reducing the data sprawl that drives compliance risk
- Delivering real-time API responses without retaining or redistributing your customer data
- Enabling privacy-safe enrichment so your teams can act on insights without expanding your PII footprint unnecessarily
If your organization is working to strengthen its PII management practices ahead of regulatory scrutiny, we would love to help. Contact us to explore how our identity resolution platform can support your compliance goals.